Next-generation security operations system based on big data
A system that detects, collects, and shares internal and external cyber threat intelligence for rapid response to security incidents
Introduction
We built a “next-generation security operations system based on big data” for real-time analysis and proactive response, as cyberattacks related to inter-Korean unification grow more sophisticated and more frequent.
The security operations system we built has the following features.
1. ADMS
An automated crawling system driven by keyword input collects recent trends and issues, and the information stored through classification modeling can then be used during security analysis.
The system is built so that security incident events and the current trends it has collected can be analyzed at the same time.
- Automated crawling system for client-tailored information, built on big data and driven by keyword input
- Comparison of crawled data against the data the client holds
- Collection of recent trends and issues, or of client-tailored information
- Classification of information similar to the client’s information through classification modeling
- Visualization of categorized data based on inferred client needs
2. Information sharing portal
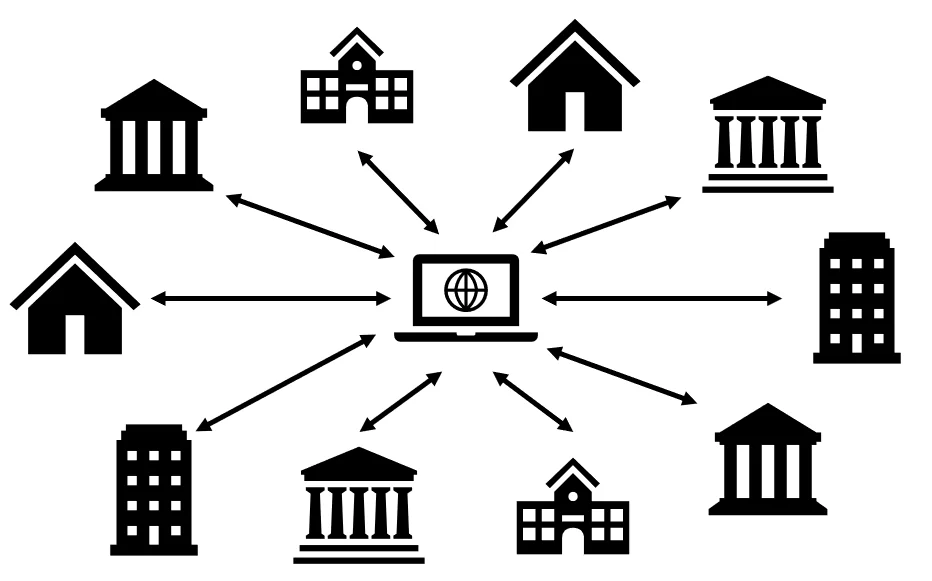
Work status and information from related agencies or individual departments are shared in real time, providing an environment for closely coordinated collaboration and maximizing work efficiency.
3. Work management system
This system was built to make the features listed above easy to manage at a glance. Its user-friendly UI makes a wide range of data easy to manage and shows the progress of each feature.
Vulnerability assessment targets, items, and results can be managed and their statistics viewed, enabling internal asset management through threat detection. Plans for the user organization’s work, such as tasks, training, meetings, duty status, and other schedules, can be managed all in one place, easily and conveniently.